| New Threats Detection Added | • Matanbuchus • NetSupport RAT • Coruna • Bad Candy |
| Newly Detected Threats | 13 |
| New IDPS Rules Created | 63 |
Weekly Detected Threats
The following threats were added to Crystal Eye this week:
Threat name: | Matanbuchus | |||||||||||||||||||||||||||
Matanbuchus, Malware-as-a-Service (MaaS), is a loader first discovered in 2021, which targets Windows-based operating systems. Matanbuchus malware primarily downloads and executes additional payloads such as ransomware, remote access trojans (RATs), Cobalt Strike beacons, and information stealers. Attackers distribute it through malicious phishing emails, malicious downloads, and malvertising campaigns. This malware also has capabilities, including in-memory execution, PowerShell execution, scheduled task creation, and command-and-control (C2) communication to avoid detection and maintain persistence. | ||||||||||||||||||||||||||||
Threat Protected: | 04 | |||||||||||||||||||||||||||
Rule Set Type: |
| |||||||||||||||||||||||||||
Class Type: | Command-and-Control | |||||||||||||||||||||||||||
Kill Chain: |
| |||||||||||||||||||||||||||
Known Exploited Vulnerabilities (Week 4 - October 2026)
For more information, please visit the Red Piranha Forum:
https://forum.redpiranha.net/t/known-exploited-vulnerabilities-catalog-4th-week-of-october-2026/707.
Vulnerability | CVSS | Description | Affected Version | Fixed Version |
9.9 | SQL Injection - Arista VeloCloud Orchestrator (on-prem) contains an SQL Injection vulnerability that can allow an authenticated remote attacker to obtain elevated privileges on the system. | 5.2.0 - 5.2.3.16 6.1.0 - 6.1.3.7 6.4.0 - 6.4.2.8 | 5.2.3.18 6.1.3.10 6.4.2.12 | |
9.2 | Unauthenticated RCE - Collabora Online - Built-in CODE Server contains an OS command injection vulnerability that when used within the NextCloud platform can allow an unauthenticated remote attacker to execute operating system commands on the system. | <= 26.4.302 | 26.4.303 | |
8.5 | RCE - EG Secure Solutions SiteGuard contains an OS command injection vulnerability that can allow an attacker to execute operating system commands with root or SYSTEM privileges on the system. | Check vendor advisory for affected products and versions. |
| |
8.6 | Authenticated RCE - Plex Media Server contains a vulnerability that can allow an authenticated attacker with administrative privileges to write arbitrary files to the system which may get executed upon startup. This vulnerability can be chained with CVE-2026-96652, CVE-2026-96654, and CVE-2026-96655. | <= 1.43.0.10492 | 1.43.3.10861 | |
4.3 | Authenticated SSRF - Plex Media Server contains a server-side request forgery vulnerability that can allow an authenticated attacker to request arbitrary internal or external addresses. This vulnerability can be chained with CVE-2026-96652, CVE-2026-96654 and CVE-2026-96656. | <= 1.43.0.10492 | 1.43.3.10861 | |
6.9 | Plex Media Server contains a vulnerability that can allow an authenticated attacker to interact with plugins with custom parameters. This vulnerability can be chained with CVE-2026-96652, CVE-2026-96655, and CVE-2026-96656. | <= 1.43.0.10492 | 1.43.3.10861 | |
5.3 | Unauthenticated SSRF - Plex Media Server contains a server-side request forgery vulnerability that can allow an unauthenticated remote attacker to send requests on behalf of the server. This vulnerability can be chained with CVE-2026-96654, CVE-2026-96655, and CVE-2026-96656. | <= 1.43.0.10492 | 1.43.3.10861 | |
6.7 | DLL Sideloading - Siemens Software Center contains a DLL sideloading vulnerability that can allow an authenticated local attacker to place a specially crafted DLL in the directory of the application which can result in arbitrary code execution on the system with privileges of the application. | < V4.0.9.8 | 4.0.9.8 | |
9.9 | SQL Injection - Arista VeloCloud Orchestrator (on-prem) contains an SQL Injection vulnerability that can allow an authenticated remote attacker to obtain elevated privileges on the system. | 5.2.0 - 5.2.3.16 6.1.0 - 6.1.3.7 6.4.0 - 6.4.2.8 | 5.2.3.18 6.1.3.10 6.4.2.12 |
ICS Advisories (Week 4 - October 2026)
Vulnerability | CVSS | Description | Affected Version | Fixed Version |
InterSystems Corporation | InterSystems IRIS for Health CVE-2026-111594 (CVSS: 8.1) | Contains a vulnerability that can allow an attacker to view transmitted data due to TLS/SSL encryption disabled by default. Transmitted data may include credentials which can be used to gain access to the system. | 2026.2.0.221 2026.1.0.235 2025.3.0.266 | N/A |
Kiloview | E3 NDI Encoder Multiple CVES (9x) (CVSS Range: 5.3 – 9.9) | Contains vulnerabilities that can allow an attacker to execute operating system commands, access information without authentication, and read files outside the intended zoneinfo directory. Successful exploitation of these vulnerabilities can result in an attacker to fully compromise the device. | < 1.30 | 1.30 |
Siemens | Software Center CVE-2026-110936 (CVSS: 6.7) | Contains a DLL sideloading vulnerability that can allow an authenticated local attacker to place a specially crafted DLL in the directory of the application which can result in arbitrary code execution on the system with privileges of the application. | < V4.0.9.8 | V4.0.9.8 |
RUGGEDCOM APE1808 Devices CVE-2026-33387 (CVSS: 4.6) CVE-2026-33388 (CVSS: 7.4) CVE-2026-33389 (CVSS: 7.5) CVE-2026-33391 (CVSS: 5.4) CVE-2026-33920 (CVSS: 3.5) | Contains vulnerabilities that can allow an attacker to access functionality without authentication, and intercept communications between the device and sensor which can reveal credentials used to access the system. | N/A | N/A | |
Industrial Edge Devices CVE-2026-44414 (CVSS: 6.8) CVE-2026-44415 (CVSS: 9.1) | Contains path traversal vulnerabilities that can allow an authenticated remote attacker to access sensitive information. | Check vendor advisory for affected products and versions. | ||
SIMATIC S7-1500 TM MFP Multiple CVEs (x377) – CVSS Range: 3.3 – 10.0 | Contains vulnerabilities within the GNU/Linux subsystem used by the device that can allow an attacker with access to the system to execute code, escalate privileges and cause a denial of service. | V1.1.1 | N/A | |
RUGGEDCOM CROSSBOW Station Access Controller CVE-2025-6965 (CVSS: 7.7) CVE-2025-70873 (CVSS: 7.5) CVE-2025-71316 (CVSS: 9.8) CVE-2026-11822 (CVSS: 7.8) CVE-2026-11824 (CVSS: 7.8) | Contains multiple vulnerabilities within the integrated SQLite component that can allow an attacker to execute arbitrary code, obtain sensitive information and cause a denial of service. | < V6.0 | V6.0 | |
SIMATIC S7 PLCs Web Server Multiple CVEs (x7) – CVSS Range: 6.1 – 9.6 | Contains vulnerabilities that can allow an authenticated attacker to execute JavaScript within a user’s browser session when parsing specially crafted CSV files. | Check vendor advisory for affected products and versions. | ||
WinCC | Contains a vulnerability that can allow an authenticated remote attacker with database access to escalate privileges and execute code on the system. | V7.5 V8.0 – V8.0 Update 11 V8.1 – V8.1 Update 7 | N/A V8.0 Update 11 V8.1 Update 7 | |
RUGGEDCOM CROSSBOW Multiple CVEs (x11) – CVSS Range: 4.3 – 8.8 | Contains vulnerabilities that can allow an attacker to bypass authentication and gain access to the system and execute arbitrary SQL queries through SQL Injection vulnerabilities. | < V6.0 | V6.0 | |
SIMATIC S7-1500 CPU 1518(F)-4 PN/DP MFP Multiple CVEs (x428) – CVSS Range: 3.3 – 10.0 | Contains vulnerabilities within the GNU/Linux subsystem used by the device that can allow an attacker with access to the system to execute code, escalate privileges and cause a denial of service. | <= V3.1.7 | N/A | |
SIMATIC S7 Webserver API CVE-2026-85114 (CVSS: 7.5) CVE-2026-85115 (CVSS: 5.5) | Contains a path traversal vulnerability that can allow an attacker to write files to arbitrary locations. Additionally, an attacker with access to logs can obtain credentials used to authenticate to the PLC. | <= V3.3.61 | V3.3.62 | |
Industrial Edge Device Kit CVE-2026-44414 (CVSS: 6.8) CVE-2026-44415 (CVSS: 9.1) | Contains path traversal vulnerabilities that can allow an authenticated attacker to access sensitive information which can be used to gain further access to the system. | Check vendor advisory for affected products and versions. | ||
APOGEE, TALON and Desigo PXC/PXM Products CVE-2026-89208 (CVSS: 5.3) CVE-2026-102073 (CVSS: 8.2) CVE-2026-102074 (CVSS: 7.5) CVE-2026-102075 (CVSS: 7.5) CVE-2026-102076 (CVSS: 7.5) | Contains vulnerabilities that can allow an unauthenticated remote attacker to cause a denial of service and read data stored in memory. | Check vendor advisory for affected products and versions. | ||
Contains a hardcoded cryptographic key that can allow an attacker with physical or administrative access to the device to bypass UEFI Secure Boot protections. | Check vendor advisory for affected products and versions. | |||
Contains an out-of-bounds write vulnerability that can allow an attacker to crash the system. | Check vendor advisory for affected products and versions. | |||
SENTRON 3NA COM Fuse | Contains a vulnerability that can allow an attacker to trigger a denial-of-service condition through sending a network management message. | < V5.2 | V5.2 | |
Contains an out-of-bounds read vulnerability that can allow an unauthenticated remote attacker to read memory beyond the intended packet boundaries. | 431-422 R20-11 < V2303 | N/A V2303 | ||
Industrial Edge App Publisher CVE-2026-78556 (CVSS: 7.4) CVE-2026-78557 (CVSS: 8.3) | Contains a vulnerability that can allow an attacker to execute arbitrary code on the system when rendering specially crafted data, additionally a improper certificate validation vulnerability can allow an attacker to intercept, and relay captured communications between the client and server. | < V1.27.9 | V1.27.9 | |
Moxa | AIG-302 ThingsPro Edge CVE-2026-109812 (CVSS: 6.8) CVE-2026-109813 (CVSS: 8.1) | Contains vulnerabilities that can allow an authenticated attacker to gain access to sensitive information. Additionally, a hard-coded cryptographic key can allow an unauthenticated attacker to compromise the confidentiality and integrity of communications. | <= 1.4.0 | 1.4.1 |
HMS Networks | PEAK-System PCAN Windows drivers Multiple CVEs (x6) – CVSS Range: 5.0 – 7.8 | Contains vulnerabilities that can allow an attacker to cause a denial of service on the system. | <= 5.1.2 | 5.1.4 |
Hitachi Energy | MicroSCADA X SYS600 CVE-2026-9852 (CVSS: 5.0) CVE-2026-9853 (CVSS: 7.8) CVE-2026-9854 (CVSS: 7.8) | Contains vulnerabilities that can allow an attacker to inject malicious data into spreadsheets which may lead to code execution on the system. Additionally, contains vulnerabilities that can allow any local user to read and modify application objects without authentication, and escalate to administrative privileges. | <= 10.7 | 10.8 |
Updated Malware Signature (Week 4 - October 2026)
Threat | Description |
LunexStealer | LunexStealer is a Windows-based information stealer designed to steal browser credentials, authentication tokens, cookies, cryptocurrency wallet data, and system information. This is being distributed through ClickFix-style fake CAPTCHA or Cloudflare verification pages that are being hosted on compromised websites. This malware can also bypass User Account Control (UAC), abuse vulnerable drivers (BYOVD) and disable security tools before deploying the stealer payload. |
| Ransomware Report | |
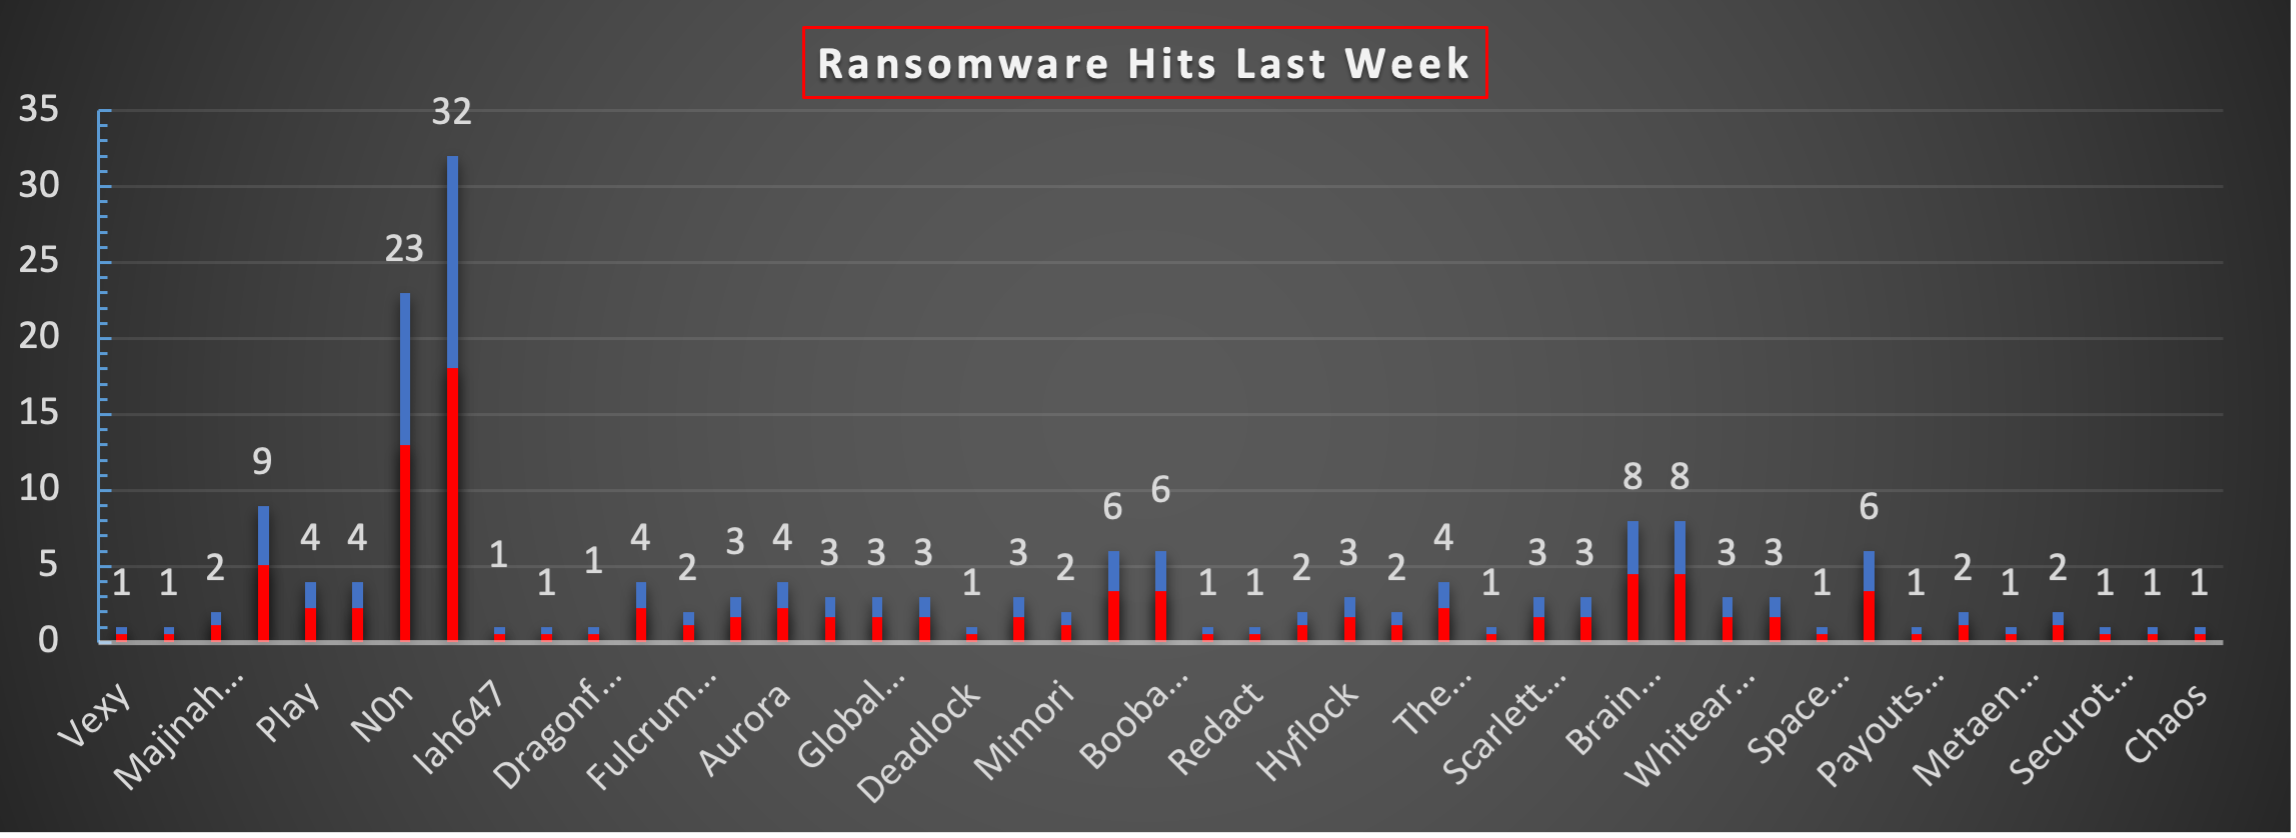
The Red Piranha Team conducts continuous surveillance across the dark web and other threat intelligence channels to identify global organisations impacted by ransomware attacks. In the past week, this monitoring revealed multiple ransomware incidents spanning a diverse range of threat groups, underscoring the persistent and widespread nature of today's cyber threat landscape. Presented below is a detailed breakdown of ransomware group activity, victim geographies, and targeted industries observed during this period. Ransomware Hits Last WeekQilin was the most active ransomware group last week, accounting for 32 victims (18.08%) of all reported ransomware attacks. N0n followed with 23 victims (12.99%), while Everest recorded 9 victims (5.08%). Brain Cipher and Akira each reported 8 victims (4.52%), placing them among the five most active ransomware groups during the reporting period. Lockbit5, Booba Team, and Lamashtu each recorded 6 victims (3.39%), demonstrating continued ransomware activity across multiple threat groups. Play, Bravox, Emperador, Aurora, and The Gentlemen each accounted for 4 victims (2.26%), contributing further to the overall ransomware landscape. Several ransomware groups recorded moderate activity, with Leakeddata, Storm, Global Secret Group, Inc Ransom, Dark Project, Hyflock, Scarlettgroup, Interlock, Whitearmor, and Rhysida each reporting 3 victims (1.69%). These groups collectively contributed a notable share of ransomware incidents, reflecting the continued presence of multiple active threat actors. Among the groups with lower victim counts, Majinahanashi, Fulcrumsec, Mimori, Payload, Pear, Orova, and Audit Team each recorded 2 victims (1.13%). Although their individual shares were relatively small, their activity further demonstrates the diversity of ransomware groups operating during the week. The remaining ransomware groups each recorded 1 victim (0.56%). These included Vexy, Byod, Iah647, Eclipse, Dragonforce, Deadlock, Anubis, Redact, Clop, Space Bears, Payoutsking, Metaencryptor, Securotrop, Wallstreet, and Chaos. |
Worldwide Ransomware Victims
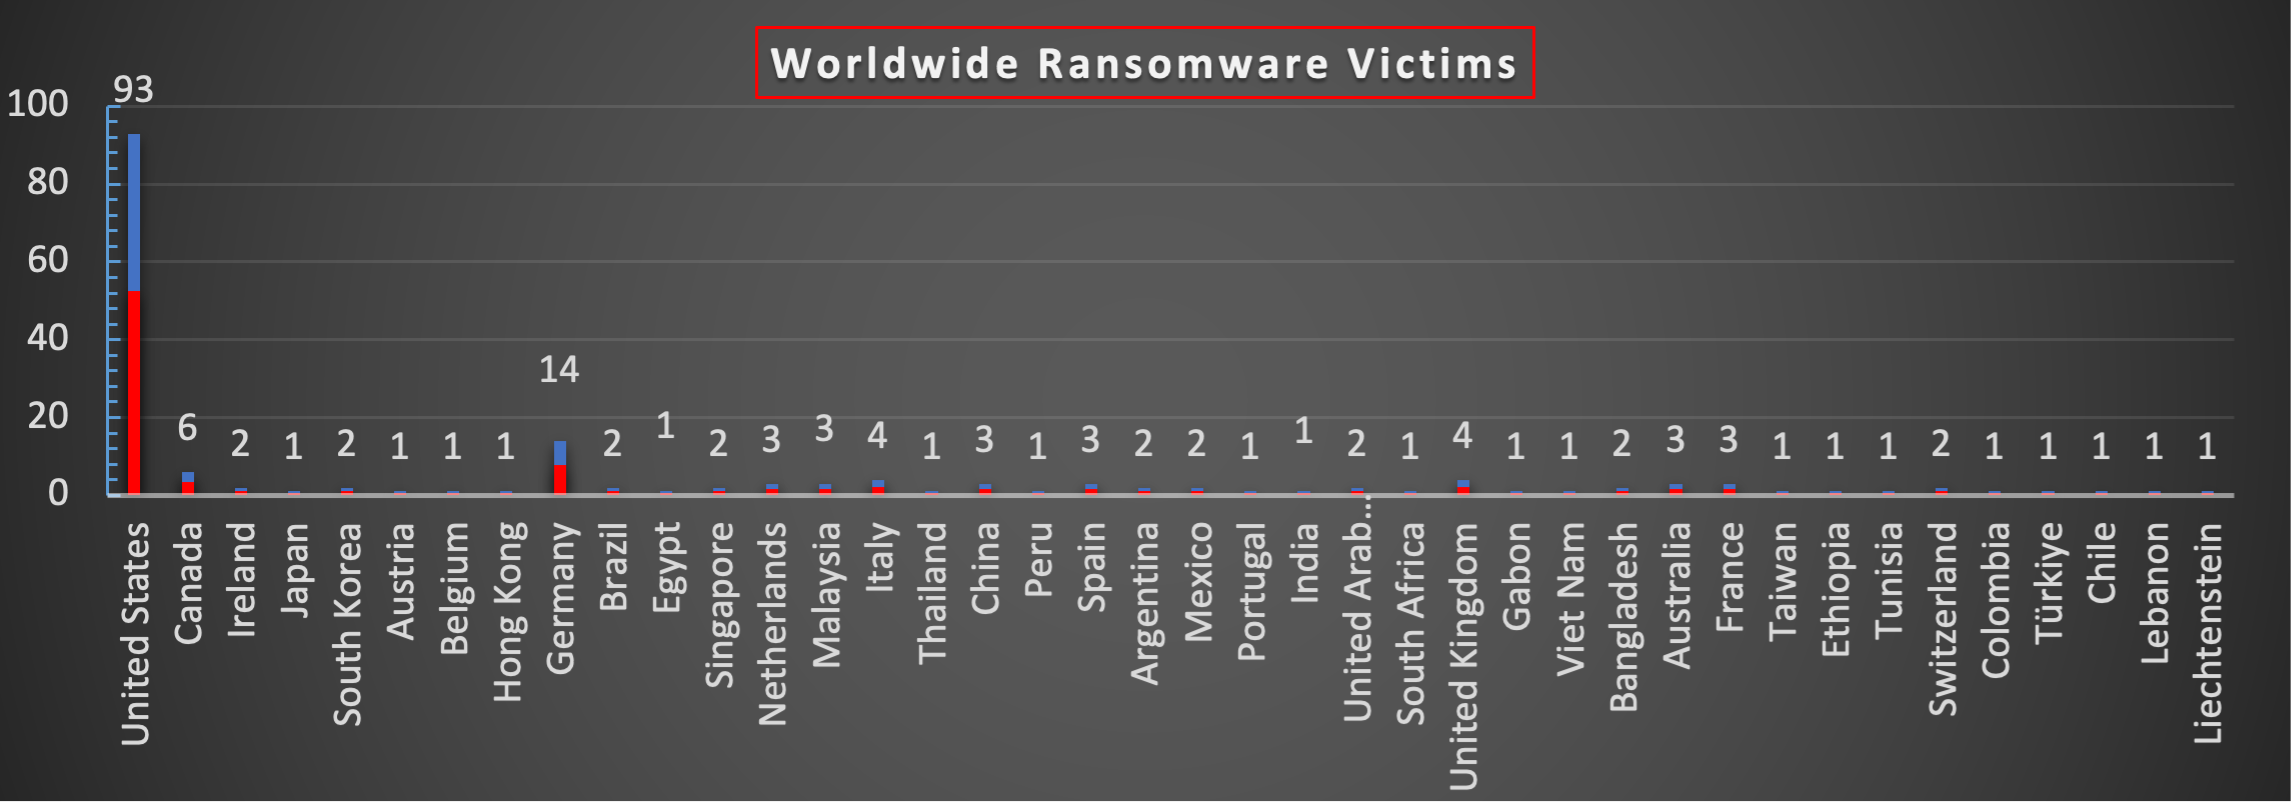
The United States was the most affected country, accounting for 93 ransomware victims (52.54%) of all reported ransomware attacks worldwide. Germany followed with 14 victims (7.91%), making it the second most affected country. Canada recorded 6 victims (3.39%), while Italy and the United Kingdom each reported 4 victims (2.26%), highlighting the significant concentration of ransomware activity across North America and Europe.
Several countries experienced moderate ransomware activity, with the Netherlands, Malaysia, China, Spain, Australia, and France each recording 3 victims (1.69%). These figures demonstrate the continued impact of ransomware across European and Asia-Pacific countries, alongside other regions.
Countries reporting 2 victims (1.13%) included Ireland, South Korea, Brazil, Singapore, Argentina, Mexico, the United Arab Emirates, Bangladesh, and Switzerland. Although their individual shares were relatively small, these countries contributed to the overall geographic distribution of ransomware incidents during the reporting period.
The remaining countries each recorded 1 ransomware victim (0.56%). These included Japan, Austria, Belgium, Hong Kong, Egypt, Thailand, Peru, Portugal, India, South Africa, Gabon, Viet Nam, Taiwan, Ethiopia, Tunisia, Colombia, Türkiye, Chile, Lebanon, and Liechtenstein.
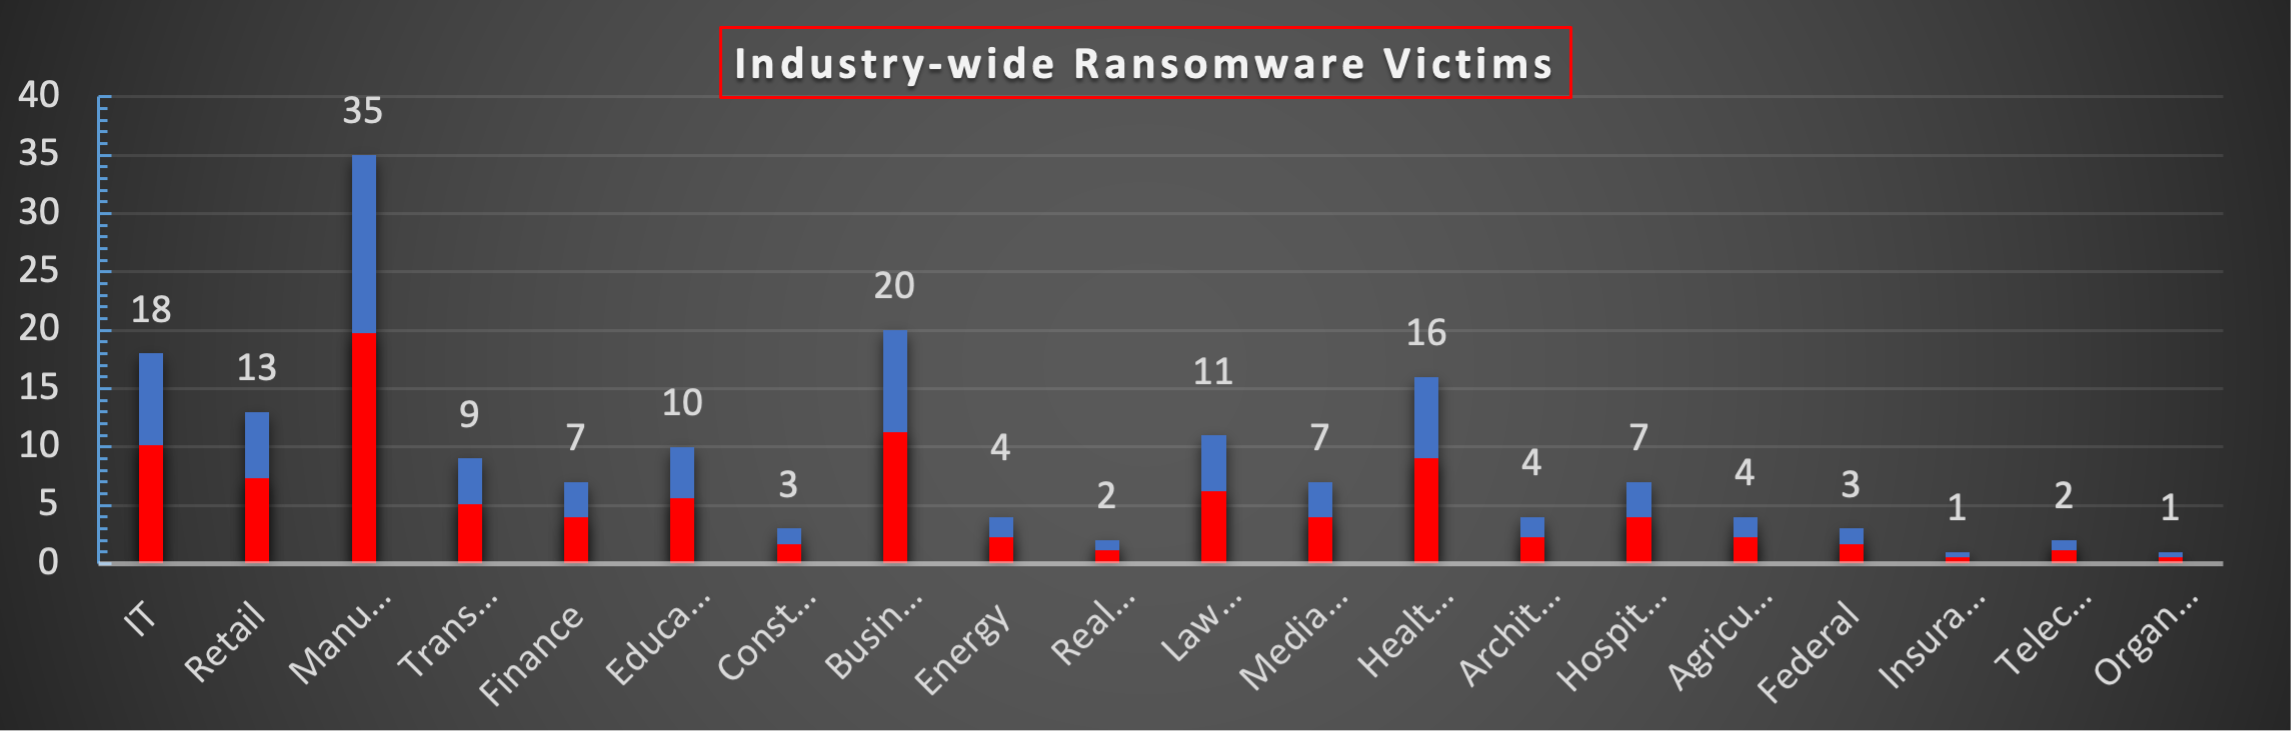
Industry-wide Ransomware Victims
Manufacturing was the most affected industry, accounting for 35 ransomware victims (19.77%) of all reported ransomware attacks. Business Services followed with 20 victims (11.30%), while IT recorded 18 victims (10.17%). Healthcare accounted for 16 victims (9.04%), and Retail reported 13 victims (7.34%), highlighting the significant impact of ransomware across industrial, commercial, and technology-driven sectors.
Among the other significantly affected industries, Law Firms recorded 11 victims (6.21%), followed by Education with 10 victims (5.65%) and Transportation with 9 victims (5.08%). Finance, Media & Internet, and Hospitality each reported 7 victims (3.95%), demonstrating the continued presence of ransomware threats across professional services, financial institutions, and consumer-facing businesses.
Several industries experienced moderate ransomware activity, with Energy, Architecture, and Agriculture each recording 4 victims (2.26%). Construction and the Federal sector each accounted for 3 victims (1.69%), reflecting the continued exposure of infrastructure-related industries and government organisations to ransomware attacks.
Among the industries with lower victim counts, Real Estate and Telecommunications each reported 2 victims (1.13%). Insurance and Organisations recorded 1 victim each (0.56%). Although these sectors represented smaller shares of the overall ransomware activity, their inclusion demonstrates that ransomware threats extend across a wide range of industries.
The Seven Deadly Sins Ransomware
Group Overview
Red Piranha identifies The Seven Deadly Sins (7DS, TSDS) as a data-theft extortion crew, not an encrypting ransomware group. The operator says it does not use ransomware; no encryptor, note, extension or sample has been observed. [1][2][3][4]
Its business model, breaking into a cloud software supplier and walking through that supplier's connections into customers' Salesforce data, is the one the ShinyHunters extortion crews made their own. And its leak servers are laid out like theirs: stolen data sits under a folder called /pay_or_leak/, each victim folder holds a plain-text INFORMATION.txt describing what was taken, archives use the same 'should have paid the ransom' naming, and one mirror sits with the same Russian hosting provider (Prospero). Red Piranha assesses with MEDIUM confidence that the group reuses the ShinyHunters template and model; whether it is the same people or an imitator is UNKNOWN. [3][4][9]
The operator says it emails the target first and allows about a week to respond. The organisation is then placed on the leak site with a 48-to-72-hour countdown and a public proof sample, and an INFORMATION.txt on a separate archive server states what was taken and the deadline. After expiry the card stays 'notified, no response' or 'unreachable', or is marked 'SOLD, data sold to private buyer'; three of the seven current cards have shown that label in every capture since 15 October. The group says payment buys deletion. [3][4]
Technical Analysis
No malware sample or incident report exists for this group. The steps below come from the operator’s own leak-site text, what it told a journalist, and what two victims and one regulator confirmed. Nothing was encrypted. This is data theft followed by extortion.
Initial foothold
The group breaks into suppliers, not victims. It compromised the maker of a product-feedback tool that many companies connect to Salesforce and took the keys the tool uses to log in to each customer. Those keys opened each customer’s Salesforce directly. A second route is a company reporting dashboard (Metabase) left open to the internet, with the databases behind it.
Evidence: a victim and a regulator (424 organisations in Türkiye) confirm the Salesforce route, and two customer notices describe the stolen keys. The dashboard route is the operator’s claim, backed only by a hospital that found possible unauthorised access to a reporting system.
Access and persistence
No malware is involved. The stolen keys are the access, and they work until the supplier or the customer cancels them, which happened from 28 August. The operator also claims standing access to 300+ Jira and 50+ other business-tool accounts.
Evidence: the key theft and the cancellations are confirmed. The standing-access figures are the operator’s word only.
Discovery
Once inside, the group looks for what is worth selling. Its notes on victim pages list the contents of one reporting tool (161 users, 81 dashboards), database table names and cloud-storage file lists.
Evidence: taken from the operator’s own notes on its archive server, with no outside confirmation.
Collection and exfiltration
The group copies customer records, billing files and database tables, then packs each victim’s data into a 7z archive. The operator says it exported the confirmed victim’s Salesforce data on 26–28 August. It claims about 230 million rows and 3.8 TB in total.
Evidence: one victim confirmed only limited business-contact and contract data, and the hospital confirmed programme records only. The volumes are unverified.
Extortion
The group emails the victim, then posts a leak-site card with a 60- or 72-hour countdown and a proof sample. A card ends as expired, SOLD, or “session open” (negotiating). The operator says payment buys deletion. As of 22 October, the board shows 3 SOLD, 3 expired and 1 negotiating, and the onion site and its mirror went offline on 21–22 October for an unknown reason.
Evidence: the process is consistent across the leak site, the operator’s interview and tracker captures. No payment has been confirmed, and the claim of low-eight-figure ransoms is unverified.
MITRE ATT&CK Mapping
Only techniques evidenced by the group's own pages and statements, by a confirmed victim or regulator, or by public scans of the group's servers are mapped; where the only source is the operator, the row says so. [3][4][5][6][7][8]
| Tactic | Technique | Evidence decision |
|---|---|---|
| Resource Development | T1583.003 Acquire Infrastructure: Virtual Private Server; T1583.001 Domains (Tor service and a re-pointed clearnet domain) | Tor data-leak site, |
| Initial Access | T1199 Trusted Relationship; T1195.002 Supply Chain Compromise: Software Supply Chain | Victim confirmed access through a third-party SaaS tool's Salesforce connection; [5][6][7] |
| Initial Access | T1190 Exploit Public-Facing Application or T1078 Valid Accounts (internet-exposed BI dashboard; mechanism not stated) | Operator names an exposed Metabase instance for two listings; a hospital on the board reported possible unauthorised access to an internal reporting system identified on 21 September. [3][8] |
| Credential Access | T1528 Steal Application Access Token; T1552 Unsecured Credentials | API keys, integration credentials and hashed passwords taken from the vendor per a customer notice; CMS administrator tokens and device private keys advertised. [3][7] |
| Discovery | T1526 Cloud Service Discovery; T1087 Account Discovery | OPERATOR-CLAIMED (MEDIUM). Connected warehouses, dashboard users and dashboards enumerated; CRM record types named. [1][3] |
| Collection | T1213.004 Data from Information Repositories: CRM Software; T1530 Data from Cloud Storage | OBSERVED (HIGH) for CRM, confirmed by the victim; warehouse, data-lake and object-store tables OPERATOR-CLAIMED. [1][3][5] |
| Exfiltration | T1567 Exfiltration Over Web Service | OPERATOR-CLAIMED (MEDIUM). Row counts on every card; about 3 GB provided to a journalist; method undocumented. [3][4] |
| Impact | T1657 Financial Theft (extortion) | OBSERVED (HIGH). Countdown cards, INFORMATION.txt demands, SOLD labels, email and Session contact channels. [1][2][3] |
| Impact | T1486 Data Encrypted for Impact | NOT ESTABLISHED. Operator states it does not use ransomware; no sample, note or extension has been observed; one tracker labels the group a data broker while others file it under ransomware. [1][4] |
Indicators and Contextual Observables
Every indicator below is specific to The Seven Deadly Sins: each was published by the group on its own pages or has been recorded by a tracker or a public scan serving those pages. Victim domains are not malicious infrastructure and are not listed. [1][2][3][10]
| Type | Defanged value | Classification |
|---|---|---|
| Leak-site onion (DLS) | sinsp6ibw32abbcoagbjwetgm2w56u7tr4izy3xzp7ehqoenxvdd3qyd[.]onion | ASSOCIATED, HIGH. Title 'The Seven Deadly Sins | DLS'; nginx; last seen reachable by a tracker on 21 October at 22:05 UTC and recorded as unavailable from 21 to 22 October. [1][2] |
| Clearnet mirror (live board) | hxxp://185.100.85[.]146/ (/, /archives/ | ASSOCIATED, HIGH. Served the live board 15 to 20 October; AS200651 FlokiNET (RO); returned HTTP 503 on 22 October; VirusTotal 3 malicious of 92. [2][3][10] |
| Clearnet mirror (September board) | hxxp://193.24.123[.]177/ | ASSOCIATED, HIGH. Serves a static copy of the 21 September board (eight cards, 24 September deadlines) on nginx 1.24.0, last modified 23 September; AS200593 Prospero (RU); VirusTotal 4 malicious of 92. [3][10] |
| Clearnet mirror (intermittent) | hxxps://37.72.140[.]179/ | ASSOCIATED, HIGH. Served the eight-card board to a public scan on 21 October 15:53 UTC; otherwise unreachable; AS211663 GALEON (RU); VirusTotal 2 malicious of 92. [2][3][10] |
| Archive node | hxxp://37.77.150[.]177:8080/pay_or_leak/ | ASSOCIATED, HIGH. Hosts INFORMATION.txt and proof samples for every card plus one folder not on the board; 'Index of /pay_or_leak/' on public scans 16 and 17 October; AS198953 Proton66 (RU); VirusTotal 7 malicious + 3 suspicious of 92; the domain is a 2019 registration now resolving here, 8 of 92. [1][3][10] |
| Contact channels | thesevendeadlysins@tuta[.]io; Session ID 051b2734…8452d | ASSOCIATED, HIGH. Published on the identity page as the negotiation channels. [3] |
| File and path artefacts | INFORMATION.txt; EMAIL.txt (negotiation template named in one note); proof files named | CONTEXTUAL. Names used in the operator's notes; the directory and the 'should have paid the ransom' naming closely match the ShinyHunters leak servers recorded by public scans (which use underscores and their own brand suffix). [3][9] |
Leak-Site Captures


Crystal Eye CE 6.0 Mitigation and Remediation
The Seven Deadly Sins reaches its victims through software connections and exposed dashboards rather than through endpoints or phishing, so the Crystal Eye controls that matter most are the ones that find exposed services, map third-party access and catch data leaving.
· Find and close exposed dashboards and consoles - Install Vulnerability Scanning from the Marketplace (Compliance Controls > Vulnerability Scanning) and run overnight network and host scans so that business-intelligence tools, database front-ends and administrative panels reachable from the internet are flagged; then use Advanced Firewall custom security zones that block everything except approved connections, with the built-in VPN options (SD-WAN WireGuard or SSL VPN) for remote staff, so those services are reachable only from inside the Crystal Eye network.
· Keep a register of third-party connections - Use Risk Auditing (the CIS Controls v8.1 basic-hygiene IG-1 checklist, recording Software and Data assets) together with Network Map device tagging to record every SaaS integration that holds standing access to CRM, ticketing or data-warehouse platforms, and reassess them on a schedule rather than at onboarding only.
· Watch identity and application changes - Where the tenant uses Microsoft 365, use the Entra ID dashboards in M365 Risk and Compliance and Azure Threat Hunting in the Threat Hunt Dashboard to review new application registrations, consent grants and role changes, since a connected application that gains administrator rights is the Microsoft 365 equivalent of the Salesforce connected-app abuse seen here; the CRM and ticketing platforms themselves must be reviewed in their own admin consoles.
· Alert on structured data leaving the network - Run Data Loss Protection in Alert or Reject mode for files carrying card numbers, government identifiers and other structured personal data; note that exports from a cloud CRM to an attacker do not cross the gateway, so this control covers on-premises data stores and the dashboards in front of them.
Known Intelligence Gaps
Two of the nine listed organisations have confirmed an incident, and each confirmed less than the operator claims: a third-party route and a limited data set in one case, an internal reporting system holding programme records rather than the general patient base in the other. No full archive has been observed served, no bundle has been downloaded to test the stated row counts, and the one stock-exchange-listed organisation on the board has filed no US securities breach disclosure (SEC Form 8-K Item 1.05). Victim names are withheld from this report by policy and held in the analyst collection record. [1][5][8]
No vendor incident-response report exists. Every operator quotation trace to a single interview, which also contains an internal inconsistency (data exported on 26 to 28 August from a vendor said to have been attacked on 28 August). How the SaaS vendor itself was entered and what 'exposed Metabase' means in practice are undocumented. [4][7]
No ransom demand, wallet, payment or buyer is public; the 'low-8-figure' statement and the 'SOLD to private buyer' labels are operator claims; the SOLD cards carry a 23 September deadline stamp, and when the label was applied between 24 September and 15 October is not known. The ShinyHunters template overlap is an observation from public scans and the operator's own file names; no vendor has published an attribution either way. [3][4][9]
The infrastructure changed during the window without explanation: the onion and the live mirror became unreachable on 21 to 22 October, while one other address still served the September board on 22 October and a third had served it to a public scan the day before. URLhaus and MalwareBazaar checks were not completed. [2][3]
Source References
[1] Ransomware.live: The Seven Deadly Sins (7DS) group page, API victim records and leak-site captures. https://www.ransomware.live/group/the%20seven%20deadly%20sins
[2] RansomLook: The Seven Deadly Sins group page, locations and archived board captures of 20 to 22 October 2026. https://www.ransomlook.io/group/the%20seven%20deadly%20sins
[3] urlscan.io public scans of the group's clearnet mirrors and archive index, 16 to 21 October 2026, with Red Piranha analyst retrievals of the identity page (20 October) and the static September mirror (22 October) held on request. https://urlscan.io/result/01a15f2a-ba81-720c-9666-094fd2778e66/
[4] DataBreaches.net: interview with The Seven Deadly Sins spokesperson on the SaaS-vendor Salesforce breach and its other affected customers, 23 September 2026 (updated 26 September). https://databreaches.net/2026/09/23/canva-hacked-via-vendors-salesforce-instance-other-customers-affected-as-well/
[5] Cyber Daily: Australian software company confirms third-party data incident claimed by The Seven Deadly Sins, 19 October 2026. https://www.cyberdaily.au/security/14317-exclusive-aussie-software-giant-canva-confirms-third-party-data-incident
[6] KVKK (Türkiye Personal Data Protection Authority): public announcement on the data-breach notification, decision 2026/2037 of 16 September 2026. https://www.kvkk.gov.tr/Icerik/8961/kamuoyu-duyurusu-veri-ihlali-bildirimi-canva-pty-ltd
[7] Customer security notice on the third-party feedback vendor breach (API keys, integration credentials and hashed passwords retrieved; access terminated 28 August), 6 October 2026. https://discuss.circleci.com/t/security-notice-beware-of-spear-phishing/54903
[8] IT Forum (Brazil): hospital confirms unauthorised access to an internal reporting system identified on 21 September 2026 and notifies the ANPD and Federal Police, 16 October 2026. https://itforum.com.br/noticias/hospital-sirio-libanes-ataque-cibernetico/
[9] The Hunter's Ledger: ShinyHunters data leak site at 91.215.85[.]22, infrastructure, victims and attribution, 17 April 2026 (revised 16 October 2026). https://the-hunters-ledger.com/reports/shinyhunters-dls-91-215-85-22-20260417/
[10] VirusTotal domain and IP address reports for the leak-site onion, the four clearnet addresses and gumruk[.]info, and AlienVault OTX pulse 6ad1a663cd6ca4db5040ea34, 20 to 22 October 2026. https://www.virustotal.com/gui/ip-address/37.77.150.177